
Commercial Insurance
Product Capabilities
There are many types of commercial insurance products. Why? Every client’s needs are specialized. In today’s complex business environment, companies across various industries face unique risks that require tailored insurance solutions.
Coverage Without Compromise
A universal insurance model fails due to diverse business risks.
By offering a diverse range of commercial insurance products and capabilities, we ensure that each client can find coverage that aligns perfectly with their specific risk profile and operational requirements. Our comprehensive portfolio of insurance offerings is designed to address the nuanced demands of various sectors, from small businesses to large multinational corporations.
Below is a summary list of some of the commercial insurance product and service offerings that we provide. If you have a question, reach out and we can discuss in more detail.
See All 41 Capabilities →How the Portfolio Is Organized
Four Coverage Families. One Coordinated Program.
Liability & Casualty
General liability, umbrella and excess layers, workers compensation, and the casualty lines that anchor every commercial program.
Executive & Professional Risk
D&O, E&O, cyber, fiduciary, and crime coverages protecting leadership decisions, professional services, and data.
Property, Auto & Marine
Property, business income, fleet, aviation, and inland and ocean marine placements for physical assets in motion and at rest.
Specialty & Structured Risk
Captives, surety, political risk, trade credit, and the specialty markets that answer exposures standard forms never contemplated.
Why Simpson | McCrady
Market Access That Matches the Breadth of the List
An independent brokerage since 1911, with the top-tier carrier relationships and advisory depth to place every line below and coordinate them as one program.
Unsure Which Coverages Your Program Is Missing?
The Full Portfolio
Types of Commercial Insurance by Product Capabilities
Liability & Casualty
Executive & Professional Risk
Property, Auto & Marine
Featured Insights
Perspective From the Practice
Lithium-Ion Battery Handling & Storage
A best-practice guideline for preparing your facility or home for the safe use and storage of lithium-ion batteries and energy storage systems: how and why cells fail, the fast-shifting regulatory and liability landscape, and configuration-specific controls from a charging bench to a container-scale system.
A best-practice guideline for preparing your facility or home for the safe use and storage of batteries and energy storage systems.
The Growing Risk
Lithium-ion (Li-ion) and lithium-polymer (Li-Po) batteries now power nearly every corner of modern operations: cordless tools and equipment, material-handling fleets, electric vehicles, micro-mobility devices, and the large stationary energy storage systems (ESS) that stabilize power supply and support renewable generation. Their high energy density, long service life, and fast recharging have made them the default choice. Those same qualities, however, concentrate a great deal of energy into a small, chemically reactive package. When a Li-ion battery is defective, damaged, poorly stored, or improperly charged, it can fail violently, releasing intense heat, toxic gas, and a self-sustaining fire that conventional extinguishers struggle to control.
The scale of the exposure is growing with adoption. Since the start of 2025 alone, the U.S. Consumer Product Safety Commission has issued 46 recalls and safety warnings for consumer products powered by lithium-ion batteries, and several high-profile facility fires have reshaped how regulators, fire officials, and insurers view the hazard. For any organization that uses, charges, or stores these batteries in more than trivial quantities, the question is no longer whether to manage the risk, but how thoroughly.
This guideline is a practical roadmap for our clients. It explains how and why these batteries fail, summarizes the emerging legal and regulatory landscape, and lays out configuration-specific best practices for preparing your facility, from a handful of tool batteries on a charging bench to a container-scale energy storage system.
Understanding the Risk
How lithium-ion batteries fail: thermal runaway
Nearly every serious Li-ion incident traces back to a single phenomenon: thermal runaway. It begins when one cell generates more heat than it can dissipate, often because of an internal short from a manufacturing defect, physical damage such as a puncture or crush, overcharging, deep discharge, or exposure to excessive heat. As the cell heats, it ignites its own flammable electrolyte; that heat spreads to adjacent cells, which fail in turn, producing a self-reinforcing chain reaction. Because the reaction generates its own oxygen, these fires are difficult to extinguish, can reignite hours later, and react violently with water where lithium metal is present.
Critically, failure does not happen all at once. It escalates through recognizable stages, and the earlier the failure is detected, the more options remain to intervene.

Beyond fire: toxic and environmental exposure
Li-ion fires are not only a combustion hazard. Burning cells release highly toxic gases, including hydrogen fluoride (HF) and per- and polyfluoroalkyl substances (PFAS, the persistent “forever chemicals”), that can injure the eyes, skin, and respiratory system and require evacuation. Water used to fight a battery fire can become contaminated with heavy metals such as cobalt, nickel, copper, and manganese, creating a risk of soil and groundwater pollution if it is not contained. After the January 2025 Moss Landing energy storage fire in California, which destroyed roughly 55,000 battery modules, EPA soil sampling detected several of these heavy metals at levels exceeding screening standards in the surrounding area.
The emerging legal and regulatory landscape
The regulatory picture is shifting quickly, and it increasingly reaches organizations that merely handle batteries rather than manufacture them. In May 2023, the EPA advised that most lithium-ion batteries on the market today are likely to qualify as hazardous waste under the Resource Conservation and Recovery Act (RCRA) based on their ignitability and reactivity. The agency is now developing a dedicated “universal waste” category for lithium batteries, with a proposed rule anticipated in 2026 and a final rule expected in 2027. At the state level, Extended Producer Responsibility (EPR) programs are expanding. Illinois requirements took effect January 1, 2026, and California has enacted both stewardship-plan obligations (AB 2440) and a point-of-sale recycling fee (SB 1215). Meanwhile, some states impose stricter hazardous-waste thresholds than the federal baseline.
The liability exposure is equally significant. Under the federal Superfund statute (CERCLA), cleanup liability is strict, joint-and-several, and retroactive: facility owners and operators, parties that arrange for disposal or recycling, and transporters can all be named, and even sending a small volume of defective cells to a contaminated site can expose a company to a share of the full cleanup cost. Following Moss Landing, the operator entered a CERCLA settlement in July 2025 to fund a cleanup expected to take two or more years. Organizations once considered removed from battery operations, such as auto dealerships handling EV batteries or retailers managing consumer returns, can now trigger hazardous-waste obligations, and California penalties can reach tens of thousands of dollars per day, with criminal exposure for knowing violations.

Foundations: Selection, Inspection, and Built-In Safeguards
Buy quality; avoid counterfeits
The single most effective way to reduce battery risk is to keep defective cells out of your facility in the first place. Purchase tools, equipment, and batteries from reputable manufacturers whose products are certified to the applicable Underwriters Laboratories (UL) standards, and buy replacement batteries and chargers only from the original equipment manufacturer (OEM) or its authorized vendors. Counterfeit and aftermarket batteries frequently omit the internal safeguards that protect genuine cells and are a leading contributor to failures. Where your application allows, consider lithium iron phosphate (LFP / LiFePO₄) cells, a Li-ion chemistry known for greater thermal stability and lower susceptibility to thermal runaway.
Inspect on arrival and before every use
Establish a quality-control step so a designated employee inspects new batteries on delivery, and personnel check batteries before each use. Remove from service, and dispose of properly, any battery showing bulging or swelling; cracked, broken, or discolored casings; excessive heat during charging or use; hissing; leaking; or smoke or unusual odors. Multimeters and digital or infrared thermometers support periodic, documented health checks. Keep a Safety Data Sheet (SDS) on file for every battery on site; these drive correct storage, handling, and emergency response.
Rely on built-in protections, but not on them alone
Quality Li-ion batteries include layered safeguards: a separator that shuts down ion flow as temperature rises, a pressure-relief vent, thermal interrupts and fuses, overcharge and short-circuit protection, temperature sensors, cell balancing, and a Battery Management System (BMS) that monitors state of charge, temperature, and cell health and can disconnect the pack when it detects an anomaly. These features reduce risk but do not eliminate it; facility controls remain essential.
Preparing Your Facility by Configuration
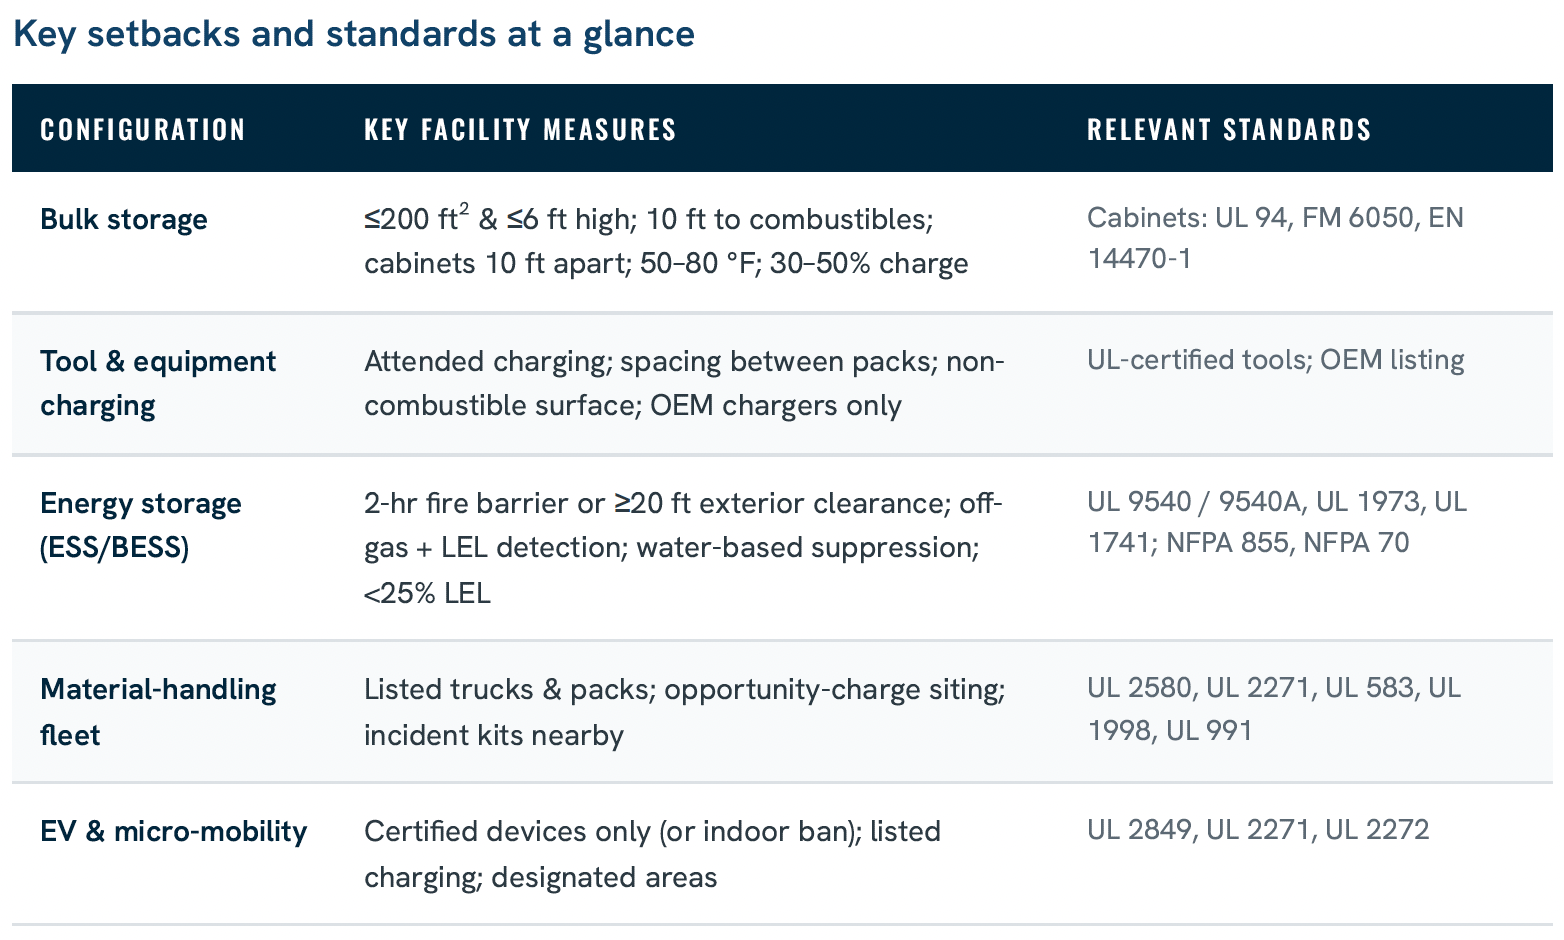
The right controls depend on how batteries are used and stored. The practices below address the configurations our clients most commonly operate; a summary of key setbacks and standards appears in the table at the end of this section.
General and bulk storage
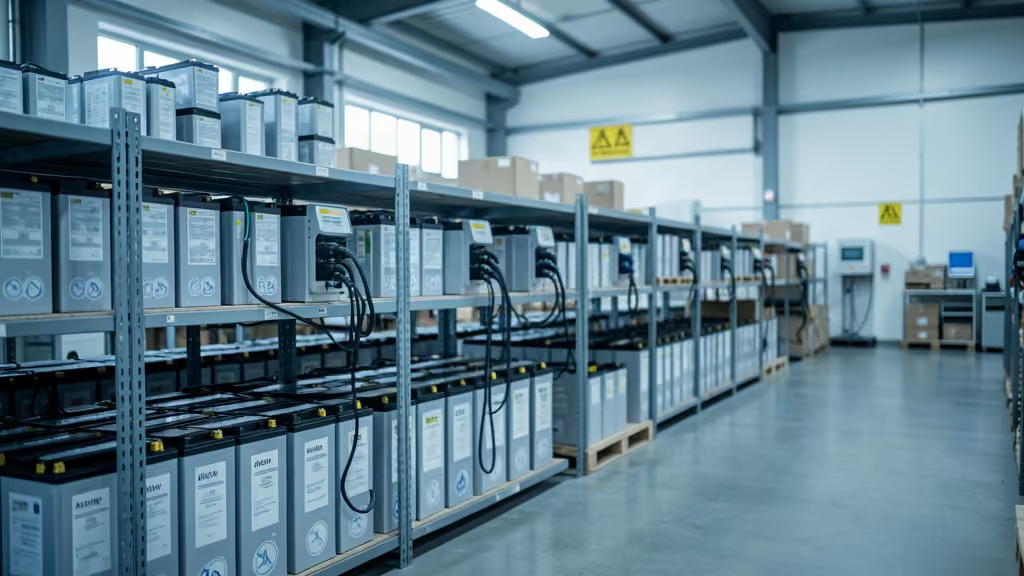
- Designate a single, controlled storage location for all Li-ion and Li-Po batteries: well-ventilated, dry, free of combustible materials, out of direct sunlight, and held at a manufacturer-appropriate temperature, generally about 50–80 °F (10–27 °C).
- For longer-term storage, keep cells at roughly a 30–50% state of charge rather than fully charged, and store only the minimum quantity needed; batteries packed closely together raise the risk that one failing cell will cascade to its neighbors.
- For larger volumes, keep quantities in high-hazard sprinklered areas incidental, limiting the battery footprint to about 200 ft² (20 m²) and 6 ft (1.8 m) in height, with roughly 10 ft (3 m) of open space to other stock and combustibles. Even a single pallet of Li-ion batteries can spread fire quickly, so consider relocating bulk quantities outdoors, to a temperature-controlled container, or to a dedicated fire-rated cabinet.
- Purpose-built Li-ion cabinets should be non-combustible (steel), fire-rated (commonly 90–120 minutes, to standards such as UL 94, FM 6050, or EN 14470-1), ventilated, fitted with pressure-relief/explosion venting and spill containment, lockable, and clearly labeled (for example, “Lithium-Ion Battery Storage: Fire Risk”); space multiple cabinets about 10 ft (3 m) apart.
- Bulk warehouse storage warrants a fire-protection engineering review, as it often requires segregated areas, in-rack sprinklers, higher ceiling sprinkler densities, and a strong water supply. Keep an ABC or Class D extinguisher (per the SDS) in the storage area.
Charging stations for tools and equipment
Most tool-battery incidents occur during charging. To avoid this:
- Charge only with the manufacturer-specified charger for that battery; never mix chargers and batteries across brands or use aftermarket chargers, which can defeat built-in protections. Locate charging on a non-combustible surface, away from egress routes and combustible storage, with space maintained between charging batteries.
- Charge only while personnel are present; do not charge unattended or overnight. Remove batteries from the charger once charged, allow hot batteries to cool before charging, and use charging bags or fire-rated charging cabinets where practical.
- Post charging and storage instructions at the station.
Energy storage systems (ESS / BESS)
Stationary energy storage introduces the largest concentration of stored energy on many sites and warrants a design-led approach. New systems should be certified to UL 9540 (Energy Storage Systems and Equipment) and evaluated using the UL 9540A test method, which characterizes thermal-runaway fire propagation and informs required spacing, ventilation, and fire protection; battery units should be UL 1973-listed and inverters UL 1741-certified. Installations should follow NFPA 855 (Installation of Stationary Energy Storage Systems) and NFPA 70 (Article 706). For further continuity:
- Detection is the linchpin. Off-gas monitoring detects electrolyte vapor at the earliest stage and can initiate an automatic shutdown and alarm before smoke or fire, while lower-explosive-limit (LEL) gas detection should be interlocked with ventilation to keep any flammable atmosphere below 25% LEL.
- For suppression, note that clean-agent gas systems generally will not stop a thermal-runaway fire; water-based protection is preferred (a wet-pipe sprinkler system, or an open-head deluge with a fire-department connection for container installations), with sprinkler density designed to at least Extra Hazard Group 1.
- Site ESS in a non-combustible, locked enclosure separated from the rest of the building by a two-hour fire barrier, or outdoors; keep exterior containers at least 20 ft from buildings unless rated thermal barriers are provided, and ensure the room is externally accessible for manual firefighting.
- Round out the design with supervised smoke detection, temperature monitoring with high-temperature alarms, coolant-leak detection, seismic bracing where required, emergency power disconnects, and clear signage. Because ESS are network-connected, incorporate cybersecurity into the BMS and firmware, and commission larger or custom systems with a qualified agent under a formal operations-and-maintenance program with online condition monitoring.
Material-handling equipment (forklifts and pallet jacks)
Electric material-handling fleets increasingly use Li-ion packs with decentralized “opportunity charging” throughout the operation. System best practices for this equipment include:
- Specify batteries and trucks listed to the relevant standards: UL 2580 for Class 1 and 2 forklifts, UL 2271 or UL 2580 for Class 3 pallet jacks, with UL 583 for the trucks and UL 1998 / UL 991 covering safety software and controls.
- Site opportunity-charging points on non-combustible surfaces, away from combustible storage.
- Report any physical damage to a battery or its enclosure immediately, and keep incident-response kits (fire blankets, gloves, non-combustible containment drums, and appropriate suppression media) near the equipment.
Electric vehicles and micro-mobility
E-bikes, e-scooters, and hoverboards are a frequent source of facility fires, and many jurisdictions now regulate them; in New York City, for example, e-bikes must be certified to UL 2849. As such, it is recommended that a policy be adopted that outlines the following:
- Either ban personal devices indoors, or allow only certified ones (UL 2849 / 2271 / 2272).
- Charge EVs with listed equipment installed by a qualified electrician, away from exits.
Emergency Response and Incident Readiness
Even well-run facilities should plan for failure. Build a written emergency response plan around the principle that early action and fast evacuation save lives and property. It is heavily recommended that the local fire department be contacted and made aware of the type, configuration, and location of battery systems within your facility. Having their insight and input into the development of your emergency response plan is vital.
Detection and isolation. Train staff to recognize the early signs (unusual odor, discoloration, swelling, excessive heat, hissing, or smoke) and, only if it is safe to do so, to move a suspect battery away from combustibles into a fire-rated isolation container. Keep a pail of sand nearby as a smothering agent.
Small, incipient fires. Because battery fires emit toxic fumes, all untrained personnel should evacuate immediately. Only personnel specifically trained to fight small battery fires should attempt to do so, positioned between the fire and the nearest exit; if the extinguisher is ineffective, smoke becomes heavy, or the responder is at all uncomfortable, they should evacuate. If flames are subdued, submerge the battery in sand or douse with water as directed by the SDS; sand is the safer choice where lithium metal may be present.
Thermal runaway and large fires. No one should attempt to fight a thermal-runaway or large-scale fire. Activate the alarm, evacuate the building, and call emergency services, providing the battery type and size, the location, and any hazardous materials present, and hand the relevant SDS to responders when possible.
First aid. For eye or skin exposure, flush with water for at least 15 minutes and seek medical attention; move anyone exposed to fumes or smoke into fresh air and administer first aid or CPR as needed. Because effects can be delayed, exposed individuals should be evaluated by a medical professional.
Disposal and cleanup. Never place Li-ion batteries in general waste; route them to a certified recycler, and store damaged units awaiting pickup in a non-combustible container located about 25 ft (8 m) from occupied buildings. Provide containment or retention basins to capture contaminated firefighting water, consistent with the environmental exposures described earlier.
Artificial Intelligence Has Changed the Cyber Threat Landscape. Here Is How You Should Be Thinking About Risk, Coverage, and Governance.
Source: Google Threat Intelligence Group (GTIG), “Adversaries Leverage AI for Vulnerability Exploitation, Augmented Operations, and Initial Access” — May 11, 2026. This memo summarizes key findings and their implications for your organization’s risk profile.
Source: Google Threat Intelligence Group (GTIG), “Adversaries Leverage AI for Vulnerability Exploitation, Augmented Operations, and Initial Access” — May 11, 2026. This memo summarizes key findings and their implications for your organization’s risk profile.
The Big Picture: What Google’s Intelligence Team Found
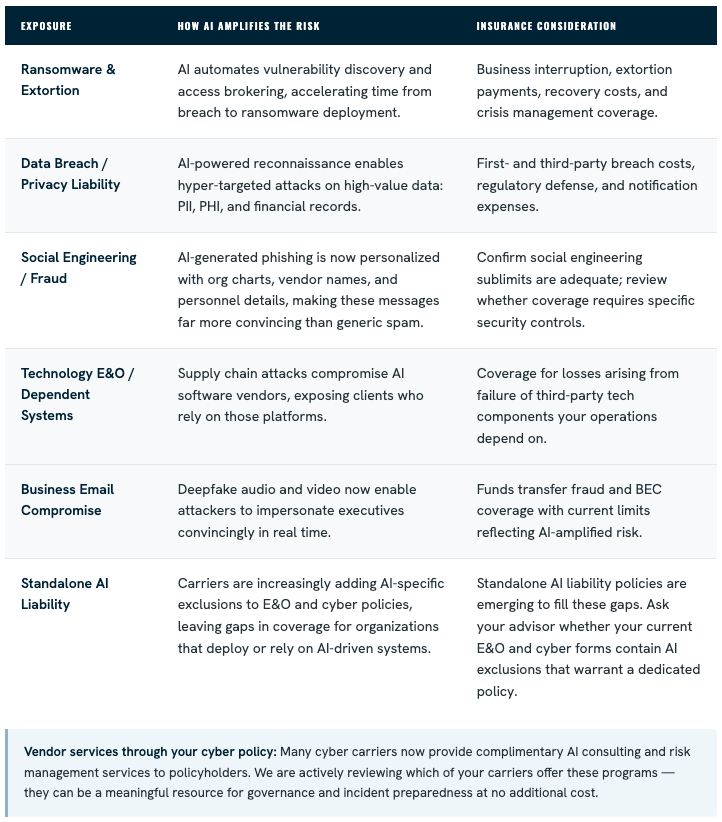
Google’s threat intelligence team published a landmark report documenting a fundamental shift in how cyberattacks are being carried out: artificial intelligence has become a standard weapon in attackers’ arsenals. The following is what the report found actively occurring:
-
-
• AI is discovering security flaws automatically: For the first time, Google confirmed that a zero-day exploit (a previously unknown vulnerability) was developed using AI. Attackers used it to plan a mass exploitation campaign targeting thousands of organizations simultaneously.
• Malware is now designed to fool your defenses: Russia-linked and other state-sponsored hackers are using AI to write malware that camouflages itself with decoy code, making it harder for traditional security tools to detect. One malware family included 32 repetitive, benign-looking code queries just to appear harmless.
• Attacks are becoming autonomous: A new Android malware called PROMPTSPY operates without human supervision: it navigates your phone’s interface, blocks uninstallation by placing an invisible overlay over the uninstall button, and can be updated remotely even if its infrastructure is identified and blocked.
• Phishing has become surgical: Attackers are using AI to research company org charts, vendor relationships, and individual employee roles before crafting personalized emails. The days of easily spotted mass-spam phishing are giving way to targeted messages that reference real people, real vendors, and real projects.
• Your AI tools are now a target: A criminal group compromised widely-used AI software packages including a popular AI gateway tool, stealing cloud credentials that were then sold to ransomware groups. If your organization uses AI software, those integrations expand your attack surface.
-
Why This Matters for Your Business
-
• The barrier to entry for sophisticated attacks has collapsed: AI has made expert-level hacking accessible to a far broader pool of adversaries. You do not need to be a Fortune 500 company to be in the crosshairs.
• Time-to-impact is compressing: AI automates the steps between initial compromise and ransomware deployment. Incident response windows that used to be measured in days are shrinking.
• No organization is too small to be a supply chain target: Attackers do not always come at you directly. They compromise a software tool you and thousands of others use, gaining access to all of you at once.
• Deepfake impersonation is operational, not hypothetical: AI voice cloning is actively being used to impersonate journalists, executives, and public figures. Business email compromise and wire fraud schemes now have an audio and video dimension.
• Your risk profile has changed even if your operations haven’t: AI has materially increased the frequency and sophistication of attacks against organizations of every size. Coverage and controls that were adequate two years ago may not reflect today’s environment.
-
-
How Insurance Responds: Key Coverage Areas to Review:
-
The Regulatory Landscape: What’s Coming and When
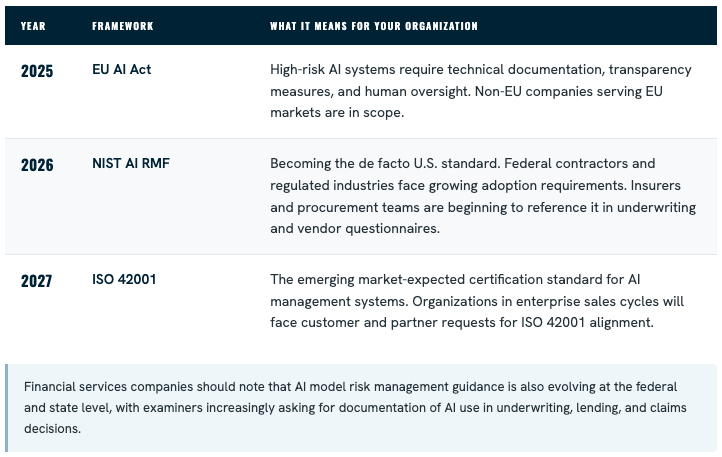
AI governance is shifting from best practice to legal obligation. The regulatory timeline is compressed, and organizations that wait for binding enforcement to arrive will face a harder and more expensive path to compliance. Cyber insurance carriers and enterprise procurement teams are increasingly referencing these frameworks in applications and vendor reviews.
-
-
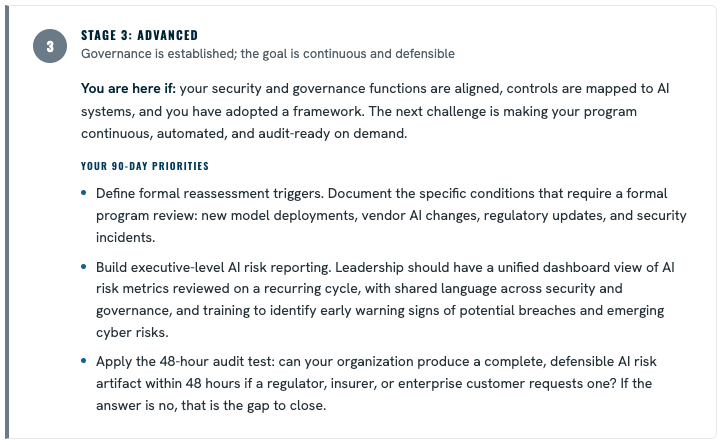
Where Does Your Organization Stand? A 90-Day Roadmap by Maturity
-
-
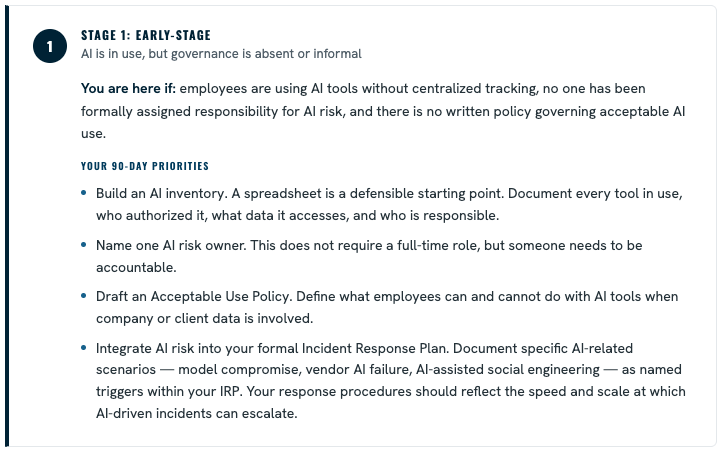
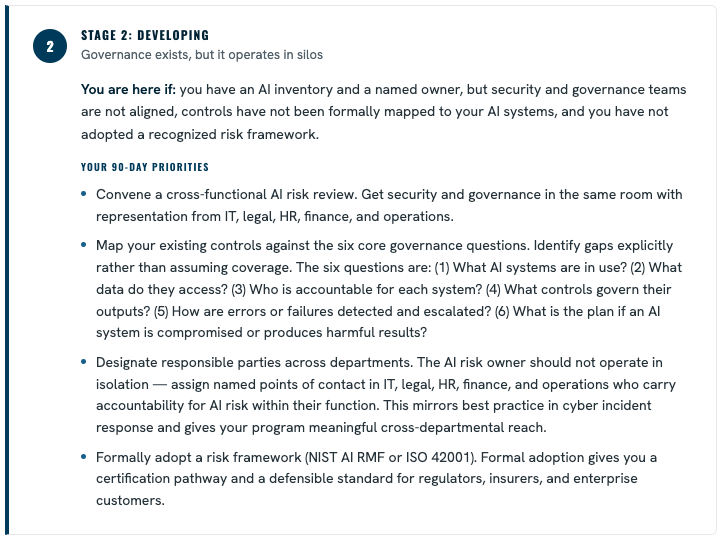
Not every organization is starting from the same place on AI governance. Identify your current stage below, then focus your next 90 days on the actions listed for that tier.
What We Recommend Discussing with Your Advisor
-
• Audit your AI software footprint: Identify every AI tool, plugin, or third-party integration in use across your organization. Each one is a potential supply chain entry point.
-
• Review ransomware sublimits: Many policies introduced ransomware sublimits in recent years. Confirm those limits still reflect your actual exposure given AI-accelerated attack timelines.
-
• Evaluate social engineering coverage: Verify your policy covers AI-generated phishing and impersonation scenarios, and confirm that coverage does not depend on security controls you may not currently have in place.
-
• Confirm your incident response plan is current: Autonomous malware and faster attack timelines demand a response plan that has been tested within the past year. One written before AI-powered threats became standard is no longer adequate.
-
• Discuss re-underwriting if your AI usage has grown: If your organization has adopted new AI tools since your last renewal, disclose that proactively. It positions you as a more credible risk and prevents coverage disputes after a claim.
Additional Resources
The following resources are recommended by practitioners and referenced by regulators and insurers:
• NIST AI Risk Management Framework (AI RMF) — The primary U.S. federal standard for AI risk governance. Free, framework-based, and increasingly referenced in procurement and insurance. airc.nist.gov • NIST AI RMF Playbook — Practical implementation guidance with mapped actions for each function of the RMF. airc.nist.gov/Docs/2 • ISO 42001 Overview — The international certification standard for AI management systems. Relevant for organizations with enterprise customers or international operations. iso.org • EU AI Act Summary — Plain-language summary of the EU regulatory framework. Relevant for any organization that operates in or sells into European markets. artificialintelligenceact.eu • CISA AI Security Guidance — Cybersecurity and Infrastructure Security Agency guidance on AI security. Practical and security-focused. cisa.gov/ai • Cranium AI Governance Platform — A purpose-built tool for AI inventory management and continuous AI risk monitoring. cranium.ai
-
-
-
Speak With an Advisor
Speak with a Trusted Advisor
One straightforward conversation is all it takes to understand where your coverage stands, and where it should be. Protecting Tomorrow Today.
Prefer to call? 412-261-2222
info@simpson-mccrady.com